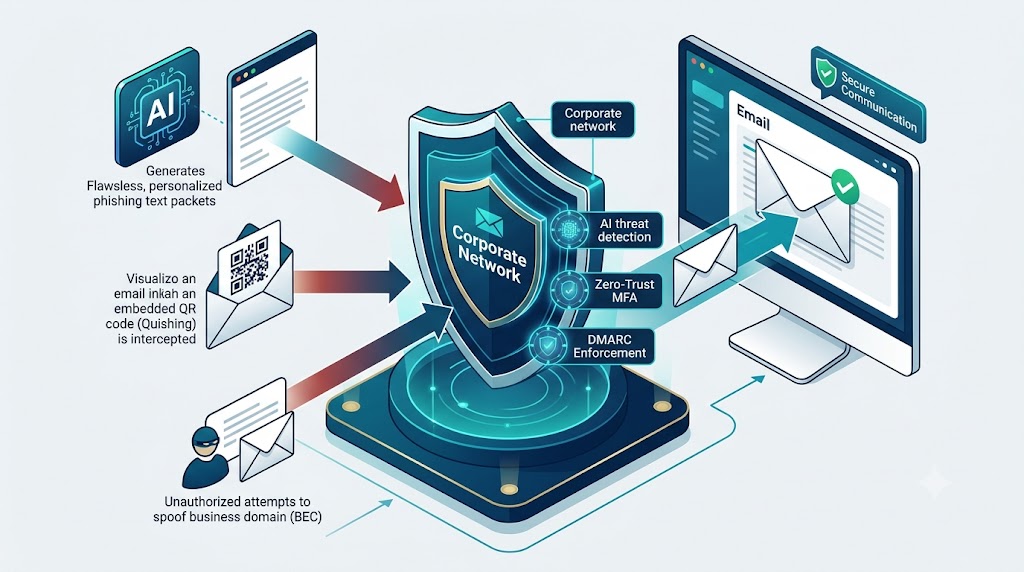

In today’s digital threat landscape, email spoofing and domain impersonation pose significant risks to corporate security. Cybercriminals frequently exploit unauthenticated domains to launch phishing campaigns, target employees with Business Email Compromise (BEC), and tarnish corporate brand reputations.
To protect your organization’s domain authority and guarantee maximum email deliverability, implementing Sender Policy Framework (SPF) is a non-negotiable security baseline.
What Is Sender Policy Framework (SPF)?
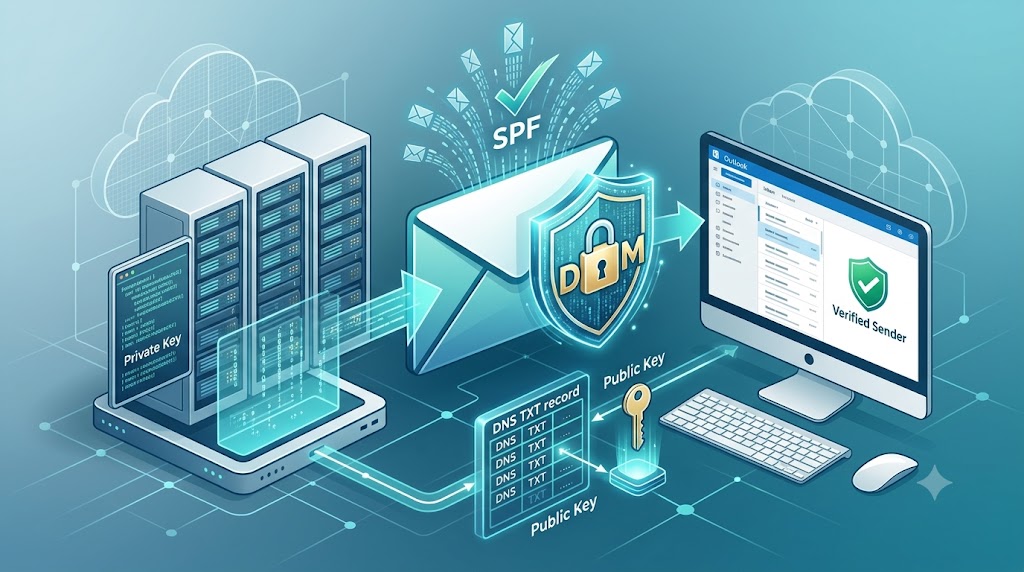
Sender Policy Framework (SPF) is an open-standard email authentication protocol designed to prevent email spoofing. It allows domain administrators to publicly declare which mail servers and IP addresses are authorized to send outbound emails on behalf of their domain.
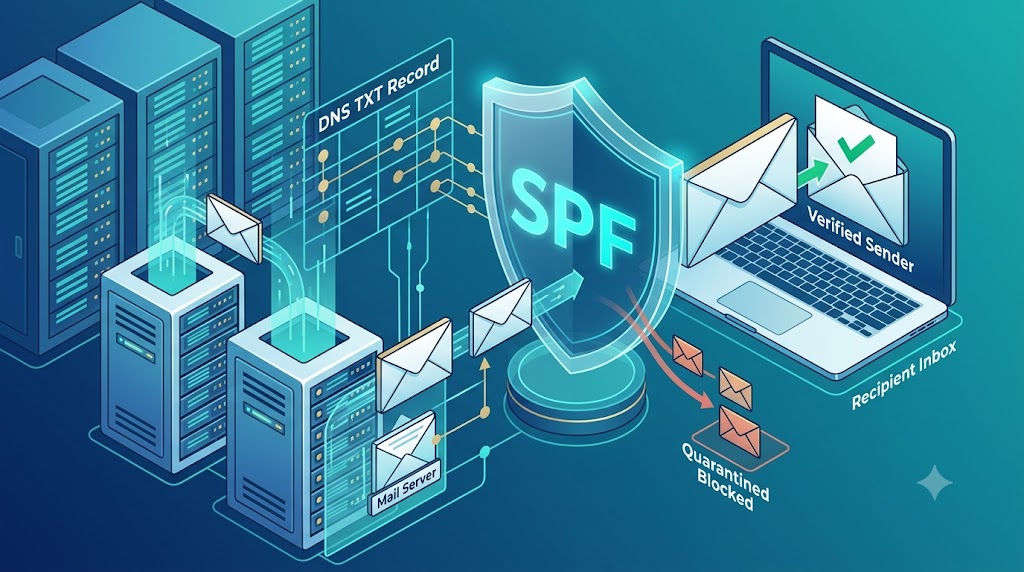
When a mail server receives an email claiming to come from your corporate domain (e.g., user@yourcompany.com), it queries your domain’s Domain Name System (DNS) TXT records to verify if the sending IP address is listed as an authorized sender.
How Does SPF Authentication Work?
The SPF validation process follows a clear 4-step execution flow:
[ Outbound Server ] ---> (Sends Email from IP 8.8.8.8)
                                │
                                ▼
                           [ Internet ]
                                │
                                ▼
[ Receiving Server ] <--- (Queries DNS for SPF Record) ---> [ Domain DNS TXT ]
        │
        ├──► IP Match Found?  ──► Pass ──► Delivered to Receiver's Inbox
        └──► IP Not Listed?   ──► Fail ──► Moved to Spam / Rejected
- Email Transmission: An outbound mail server attempts to deliver a message.
- DNS Query: The receiving mail server extracts the sender’s domain from the
Return-Pathheader and queries public DNS records. - IP Matching: The recipient server checks if the sending server’s IP address matches any IP or host listed in the domain’s SPF record.
- Enforcement Action: Based on the rule set, the email is either delivered directly to the inbox, flagged as soft-fail (spam folder), or rejected completely.
Key Benefits of Implementing SPF for Enterprise Domains
Deploying a properly aligned SPF record delivers immediate technical and operational advantages:
- Eliminates Domain Spoofing: Prevents unauthorized third parties from sending illegitimate messages using your exact business email address.
- Improves Inbox Deliverability: Major email ecosystem providers (Microsoft 365, Google Workspace) strictly filter or reject messages originating from domains without valid SPF records.
- Protects Domain Reputation: Prevents your corporate domain from being blacklisted by global Anti-Spam organizations due to unauthorized spam volume.
- Essential for DMARC Alignment: SPF works hand-in-hand with DomainKeys Identified Mail (DKIM) to achieve strict DMARC enforcement.
Understanding SPF Record Modifiers & Mechanisms
An SPF record is published as a single-line DNS TXT record.
Example SPF Record:
v=spf1 +a +mx +ip4:192.0.2.1 include:spf.protection.outlook.com ~all
Key Components Explained:
v=spf1: Declares the version of the SPF protocol being used.+a/+mx: Authorizes the domain’s primary A record and MX mail exchange servers.+ip4:: Specifies exact IPv4 addresses authorized to transmit email.include:: Incorporates third-party mail services (e.g., Microsoft 365, Google Workspace, CRM tools).
Enforcement Qualifiers (The all Tag):
The final tag defines how receiving servers should treat unauthorized IPs:
~all(Soft Fail): Email is accepted but marked as suspicious or moved to the spam folder.-all(Hard Fail): Email originating from unlisted IPs is outright rejected by the recipient server.+all(Neutral/Pass): Any IP is allowed (Not recommended for production environments).
How Xaas Techs Secures Your Email Infrastructure
Improperly configured SPF records—such as exceeding the 10-DNS lookup limit or omitting legitimate mail gateways—can accidentally cause corporate emails to bounce or land in client spam folders.
At Xaas Techs, our certified Managed IT & Cloud Security engineers manage end-to-end email authentication setups, including:
- Comprehensive auditing of corporate sending sources and IP ranges.
- Setup and maintenance of SPF, DKIM, and DMARC enforcement policies.
- Microsoft 365 and Google Workspace DNS record alignment.
- Proactive 24/7 deliverability and server monitoring for enterprises across Delhi NCR, Gurugram, and Noida.
Need Assistance Securing Your Corporate Email Domain?
Protect your business communications and eliminate spam delivery issues today. Contact Xaas Techs for a complete Email Security Audit!